In February 2016, North Korean actors reportedly compromised the Bangladesh Bank and executed a digital transfer to the tune of 81 million US dollars. The incident is frequently referenced as the clearest examples of offshore financial theft connected to hackers known as "The Lazarus Group". By May of 2017, a widespread ransomware incident identified as "WannaCry" spread across multiple countries. Public reporting and analyses have described its development and deployment as connected to North Korean state linked capabilities. While ransomware incidents are characterized by attempted payments and broad operational disruption, analyses have described the scale of infected systems as in the billions. The hackers only got away with $143,000 in bitcoin, despite the havoc caused.
Between 2017 and 2018, multiple cryptocurrency exchange related incidents were attributed to Lazarus Group activity and related North Korean criminal operations. The exchange intrusions marked the beginning of a systematic, state‑backed revenue operation: North Korean operators penetrated poorly secured exchanges, hot‑wallet infrastructure, and employee accounts to steal tens of millions in BTC and other assets, then pushed the funds through long chains of wallets and bitcoin mixers to break attribution. These early campaigns established the group’s hallmark pattern: credential compromise, social‑engineering of exchange staff, and post‑theft laundering through mixers and DEX swaps.
This pattern that later scaled dramatically as DeFi and cross‑chain bridges expanded the attack surface.
Then, in 2022, The Harmony Horizon Bridge hack was a $100M theft carried out by the Lazarus Group, caused not by a smart‑contract bug but by compromised multisig keys. The attackers drained assets across Ethereum, BNB Chain, and Harmony, then laundered them through Tornado Cash and Railgun. The progression from exchange‑level compromises to full‑scale bridge intrusions reflects a deliberate strategic shift. Lazarus began targeting the connective tissue of the crypto ecosystem, where vast pools of liquidity depend on fragile trust assumptions and centralized key management.
By 2022, their operations resembled state‑level financial warfare, blending social‑engineering, credential theft, and deep knowledge of cross‑chain architecture to strike at the most lucrative chokepoints. The Horizon incident underscored that the group no longer relied on opportunistic vulnerabilities; they actively hunted operational weak links, exploiting human processes around multisig custody rather than the code itself, and then weaponized increasingly sophisticated laundering pipelines to convert stolen value into usable state revenue.
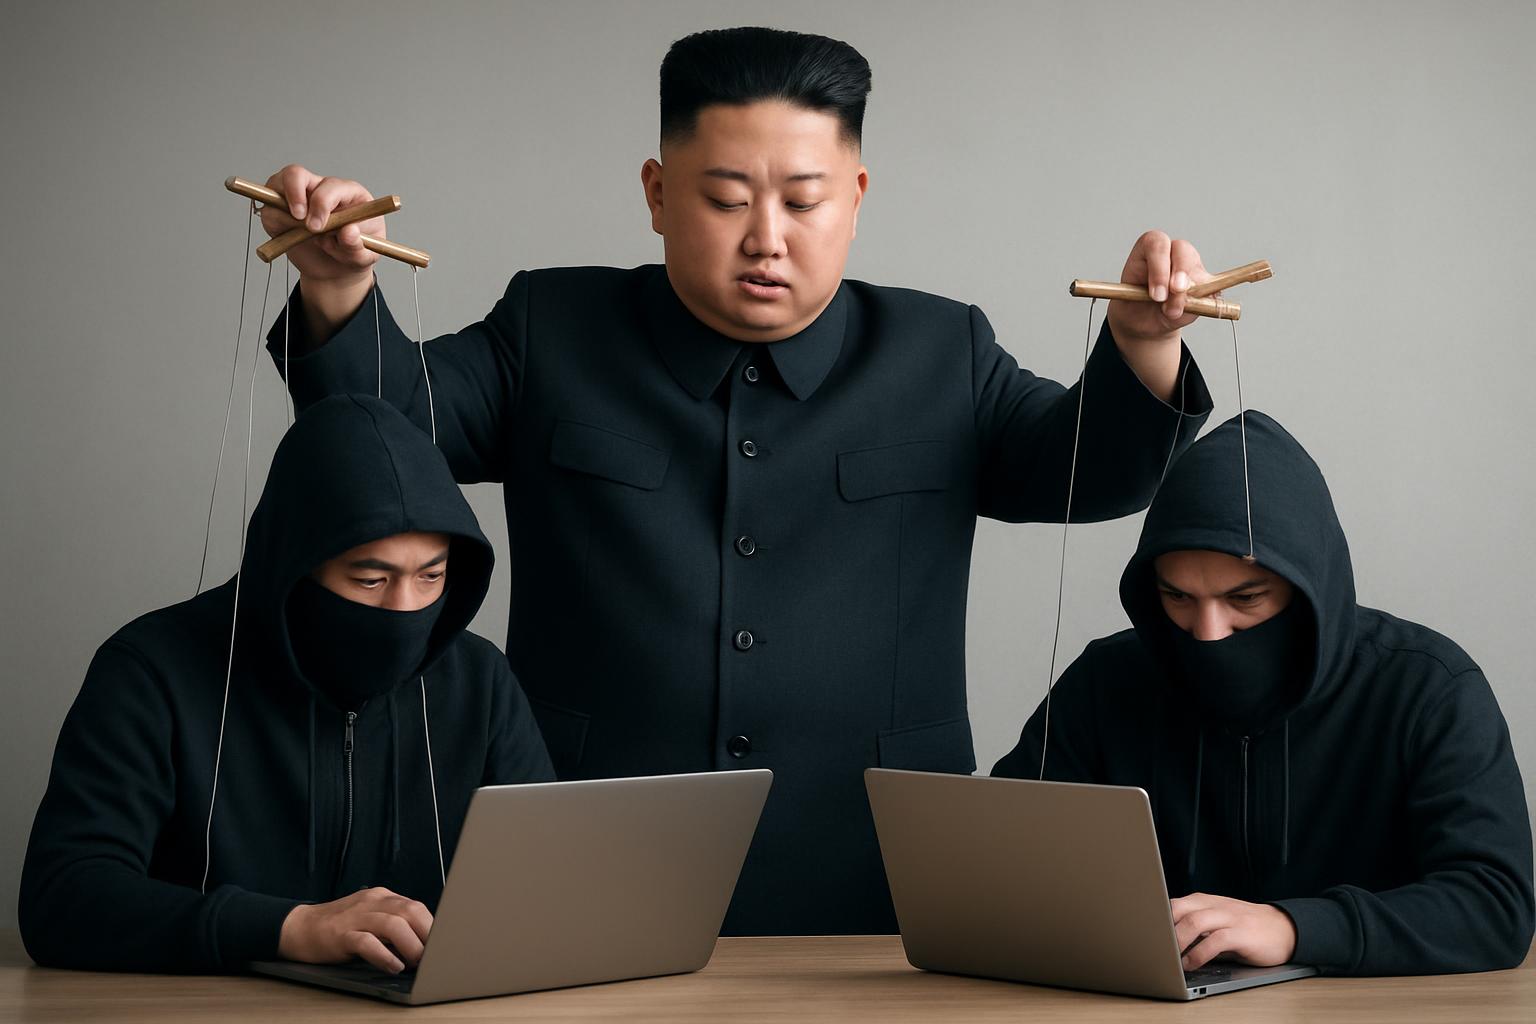
Today, Lazarus remains one of the most active and dangerous state‑sponsored cyber units in the world, continuing to operate under the direction of the North Korean government and responsible for significant harm, financial loss, and human‑rights‑impacting activity. Their operators are believed to be dispersed across North Korea and abroad, working through front companies, contractor networks, and false identities to blend into global developer and security communities while quietly probing crypto, fintech, and defense‑adjacent infrastructure. Despite sanctions, seizures, and increased blockchain‑forensics pressure, the group has adapted rather than retreated, shifting toward privacy‑focused chains, layer‑2 ecosystems, and more complex laundering pipelines, ensuring they remain a persistent threat to exchanges, bridges, and any system where human key‑management weaknesses can be exploited.
